
3 min read
How to Become Admin in QBCore
QBCore admin permissions are ACE/principal permissions, not a column in the players table.
Do not add or edit a fictional players.permission field.
The default QBCore permission names are:
godadminmod
They are configured in QBCore.Config.Server.Permissions and backed by FiveM ACE rules.
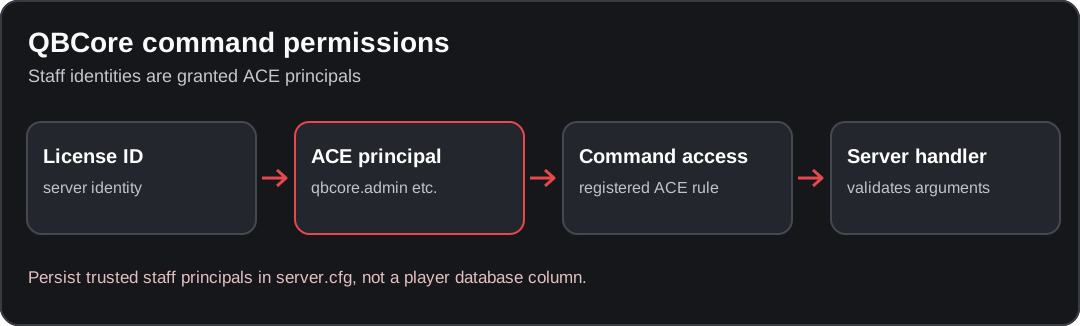
Conceptual diagram; verify the behavior against your installed resource version.
Recommended setup: persistent permissions in server.cfg
Use server.cfg for persistent staff access.
## Permissions ##

add_ace group.admin command allow

{{addPrincipalsMaster}}

# Allow qb-core to create and manage command ACEs
add_ace resource.qb-core command allow

# God can run all commands
add_ace qbcore.god command allow

# Inheritance
add_principal qbcore.god group.admin
add_principal qbcore.god qbcore.admin
add_principal qbcore.admin qbcore.mod

# Staff
add_principal identifier.license:xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx qbcore.god
add_principal identifier.license:yyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyyy qbcore.admin
The txAdmin recipe uses {{addPrincipalsMaster}} to grant the server owner its generated principal.
Keep that line when your recipe includes it.
Find the player's license
The framework uses the Rockstar/FiveM license identifier for persistent principals.
A practical way to retrieve it:
- Open the player in the txAdmin web panel.
- Inspect the player's identifiers.
- Copy the value beginning with
license:. - Add it to
server.cfgas anidentifier.license:...principal. - Restart the server or execute the relevant ACE command from the server console.
Example:
add_principal identifier.license:0123456789abcdef0123456789abcdef01234567 qbcore.adminGrant permissions in game
Current qb-core registers:
/addpermission [id] [permission]
/removepermission [id] [permission]
Examples:
/addpermission 12 admin
/addpermission 8 god
/removepermission 12 admin
These commands are restricted to god.
Internally they call QBCore.Functions.AddPermission and
QBCore.Functions.RemovePermission, which add or remove a runtime principal for the connected
player and refresh that player's command suggestions.
Runtime grants are not your persistent staff list
Use server.cfg for permissions that must survive reconnects and restarts. Treat
/addpermission as a runtime administration tool.
Use qb-adminmenu
The official administration resource is qb-adminmenu.
With the resource installed and your permission configured:
- Run
/admin. - Open Player Management.
- Select the target player.
- Open Permissions.
- Choose the intended group.
See qb-adminmenu for the resource-specific interface and Admin Commands for command ownership.
How the permission hierarchy works
The common recipe creates this chain:
qbcore.god
├─ group.admin
└─ qbcore.admin
   └─ qbcore.mod
That means a god principal inherits the admin and mod layers, while an admin principal inherits
the mod layer.
The core also creates command-specific ACEs for custom QBCore command permissions.
Add a custom permission group
The current core defines its known groups in config.lua:
QBCore.Config.Server.Permissions = { 'god', 'admin', 'mod' }To add a custom group, extend the table:
QBCore.Config.Server.Permissions = { 'god', 'admin', 'mod', 'leo' }Then grant it through ACE:
add_principal identifier.license:0123456789abcdef0123456789abcdef01234567 qbcore.leoRestrict a QBCore command to that group
QBCore.Commands.Add('spikes', 'Place spike strips', {}, false, function(source)
    -- Server-authoritative spike strip logic
end, 'leo')
For permission names other than the built-in ignore-list entries, QBCore.Commands.Add
automatically creates a command ACE equivalent to:
add_ace qbcore.leo command.spikes allowThat lets FiveM enforce the command restriction before the callback runs.
You can also grant or remove a principal dynamically from trusted server code when a role changes,
but persistent identity-based staff access belongs in server.cfg.
Verify the setup
Check the core config
Confirm the intended group exists in:
qb-core/config.luaThe current default is:
QBCore.Config.Server.Permissions = { 'god', 'admin', 'mod' }Check server.cfg
Confirm these pieces exist:
add_ace resource.qb-core command allowadd_ace qbcore.god command allow- the expected inheritance rules
- your exact
identifier.license:...principal
Check in game
After reconnecting, test a command that is actually owned by qb-core or qb-adminmenu.
Do not use a random third-party command as your permission test.
Useful checks:
/admin
/addpermission
Whether a specific command exists depends on the resources currently installed.
Troubleshooting
/admin does not exist
Check that qb-adminmenu is installed and started after qb-core.
ensure qb-core
ensure qb-adminmenu
The admin menu is not built into the core resource itself.
/addpermission says you do not have permission
The command is registered with the god permission. Verify your persistent principal first:
add_principal identifier.license:YOUR_LICENSE qbcore.godThen reconnect after the ACE configuration is loaded.
A principal works until restart, then disappears
You granted it at runtime. Put persistent staff principals in server.cfg.
You edited the database but nothing changed
That is expected if you added or edited a permission column. Current QBCore permissions are ACE
based. The framework's normal players schema does not use a permission field for staff access.
See Database schema.
A custom permission command is visible to everyone
Check all three layers:
- The custom name exists in
QBCore.Config.Server.Permissions. - The command was registered with that permission as the final argument.
- The target player has the corresponding
qbcore.<permission>principal.
Also keep:
add_ace resource.qb-core command allowso the core can create command ACEs.
Security notes
- Grant
godonly where full command access is intended. - Prefer the least-powerful permission that satisfies the staff role.
- Keep persistent principals in version-controlled or otherwise audited server configuration.
- Do not authorize privileged gameplay actions from client-supplied role or permission data.
- When adding custom commands, validate target IDs, arguments, server-side state and ownership inside the command callback as well.
Related documentation
Sources
- Official QBCore permission guide
- qb-core config.lua
- qb-core server commands
- qb-core permission functions
- QBCore txAdmin recipe server.cfg
Last verified against current upstream files: 2026-09-27.
Found an issue in this guide?
Send the page URL, the affected example, and a source or reproduction to the site maintainer. For a server or resource problem, use the support guide.
How to Create Money as Item in QBCore
Learn how to create physical money items that players can drop, trade, and pick up in your QBCore server.
QBCore Scripting Guide
Build QBCore resources with server-authorized events, a replay-resistant daily reward example, oxmysql persistence, and working NUI callbacks.
